Anyone else had issues with usps recently? My purewrist went across the country twice and was a week and a half late  my last DT order left Washington 4 days ago and still no update other than “arriving later than expected”
1 Like
I haven’t had any issues recently… but you know how usps is: if it’s convenient or works well, it’s wrong.
1 Like
Nothing too terrible for me. USPS placed a package on my mailbox at the road instead of on my porch. It’s a 1/4 mile driveway and I didn’t find it until a day later, but fortunately it was still there.
Only trouble I’ve ever had shipping wise in regards to DT was my pure wrist
Purewrist to me,
Me to DT,
DT to me,
All where slower than expected or predicted
Ups/usps/fedex hate payment conversions lol
Usps just took 6 weeks to get something (priority international) from MI to the UK … 8 days from China.
1 Like
I only know from the receiving end, but it costs about 50c to get my pay into my bank account, which is a pretty decent price. Don’t know how much Amal has to pay to send it, but the fees are significantly lower than international transfers.
Maybe purewrist are just bad luck because the same happened to me
Oh, Yeah, I should have quantified, The credit Card fees are not great, but the bank transfer looks good (Free)
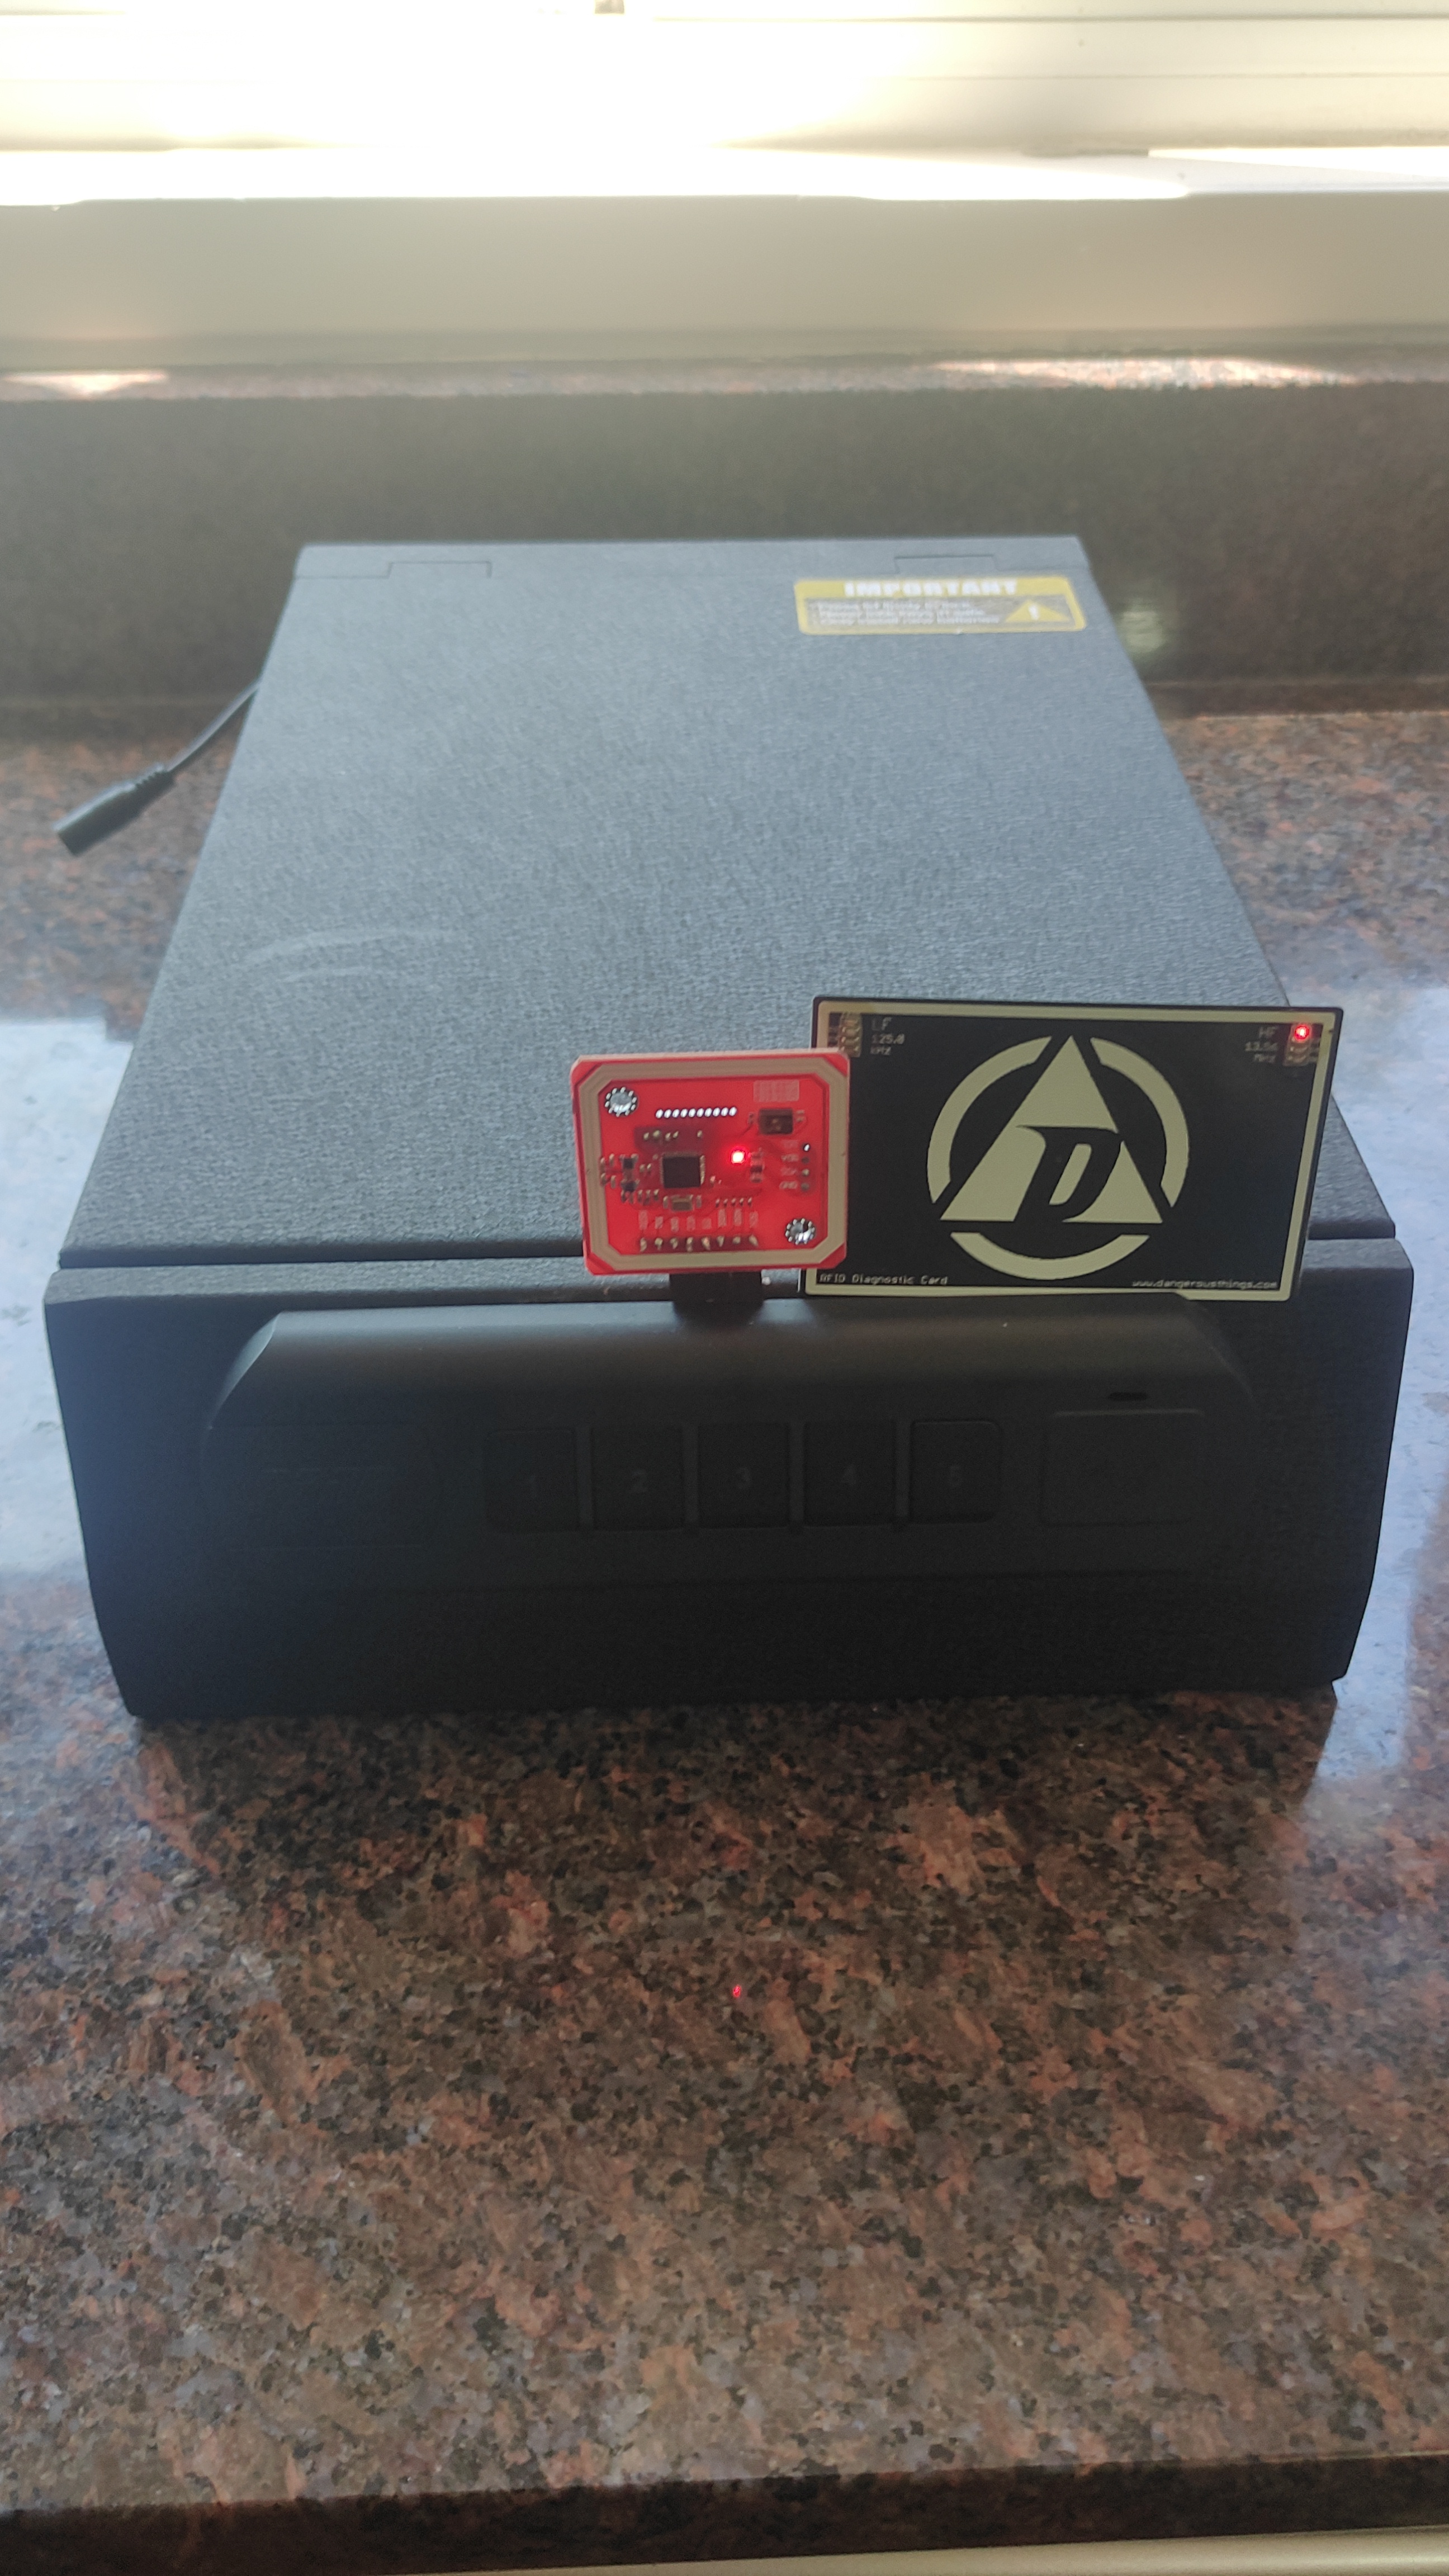
I have a question that I don’t think deserves a separate topic… Is there a security risk to having an exposed hardware SPI connection on the outside of a safe? (shown below) I’m using a ESP32 DEV KIT v1 with a PN532 to check ISO14443a UID only. The security risk I imagine is a device that pretends to be a PN532, then brute forces the correct UID faster than a PN532 could read a card spoofer. Am I being paranoid? Is there other ways a hardware SPI connection can be abused?
1 Like
A logic analyser connected between the two could capture the traffic. You would (I hope) realise it is there, but for safety sake you would be better putting the PN532 in a small (preferably tamper proof) enclosure, if you can have the enclosure cover the wiring too, even better.
1 Like
Yea I was also hoping that I could notice a logic analyzer before scanning. Is a replay attack my only worry?
1 Like
If the goal is to make that safe hard to get in, is there a backup mechanical key under either of those covers on the left and right?
Backup keys are usually hot garbage and the easiest way in
Second thing would be to strongly look at the latch mechanism to make sure it can’t be shined or actuated with a wire
Third, make sure any internal programming buttons are covered/shielded
1 Like
Yes, I was just addressing the SPI interface. Attacks via that are limited, compared to alternate mechanisms.
1 Like
Like everything, it’s a balance between difficulty, risk, and reward. There’s some level of difficulty in that an attacker would need to have proper tools and plan the proper kind of attack and have enough time to do all that in a way that’s covert without being caught or their tools being recognized and presumably confiscated… so, unless you are putting something very valuable in that safe and others would know the value, I doubt very much there is an actual security issue here. Anybody who doesn’t know the contents but wants to be able to get into it would probably just throw it on the ground hard enough that the bolts inside would got knocked open (google this).
2 Likes
Remind me to tell you the story about the RAF, the glass locking plates and the safe cracker one day…
(Short version, some squaddies decided the easiest way to move a safe was to toss it out of the second floor window into a mattress. The glass plates designed to prevent certain kinds of physical attack broke, and the safe was useless)
2 Likes
I believe this safe was on TheLockPickingLawyer’s YouTube channel. I’ve disabled the wafer lock and ripped out all the old electronics too avoid the known bypasses the video had demonstrated. I didn’t know about this “threw it on the ground” trick, I might have to look more into that  Thanks everyone for making me feal more at ease!
5 Likes
Technically there are ways to cut the wires, reconnect them to another board, then gain access…
Would depend on the invader having either knowledge of the system you’re using, or enough time to tamper enough with it. (aka: a lot of time)
So, just in case…
Albeit in all fairness, in almost all cases, there are so many vectors of attack much more efficient than the electronic one, that worrying too much about that seems kinda moot.
1 Like
Yeah, this is the “replace the reader board with a microcontroller programmed to pretend to be the reader and presenting all possible IDs as fast as possible”.
A 7 byte UID will take about 1 billion years to run through all possibilities, if you rate limit the “reader” to 2 attempts per second. If you can add a short delay to the software between accepted reads, and the controller itself is inside the case then you can pretty much mitigate the brute force attack. (Of course you would have to recalculate this for your specific UID, if they present random UIDs then they might be lucky and get in sooner, but they might be unlucky and it will be later)
1 Like
I will be implementing a short delay between reads tonight, it’s a simple and elegant solution to brute force. Thank you!
5 Likes
I particularly enjoy the exponential approach.
This allows you to have a couple of misreads without any inconvenience of a delay, but punishes way more a brute force attempt.
The trick is… You don’t need all the possibilities.
Some of these 7 bytes are usually set based on vendor and/or system, and the rest will also be “randomized” so you can avoid certain combinations which we won’t see in commercial use cards.
Therefore you can just dictionary it to shave off a lot of time out of that.
It’s funny to think that the “higher” the security standards go… the safer passwords like aaaa become. because those combinations are getting pruned from the dictionaries and bruteforce attacks.
Oh, and my favourite vector of attack if I have access to the wires, but am short on time… is the “tickle” approach. where you basically short the fuck out of the system and hope that will get you in. (It’s not as effective as throwing the safe in the ground, but surprisingly close to that!)
1 Like